Black October: The worst month in Internet history!
2 min read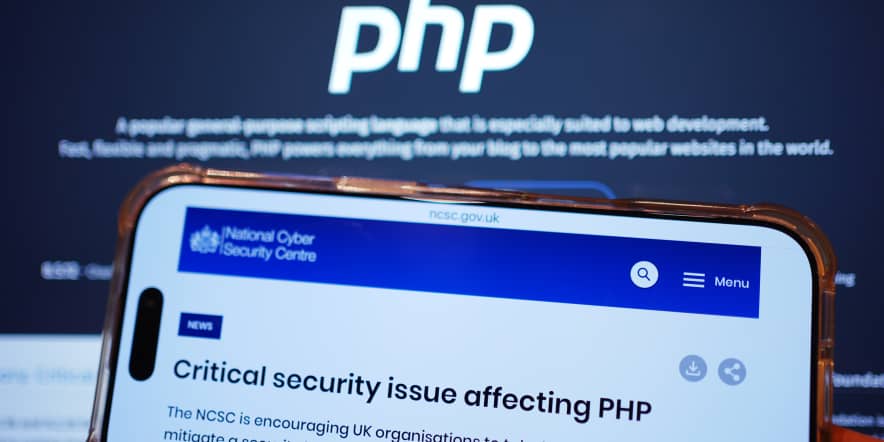
The global cybersecurity landscape is currently experiencing severe disruption in a period being dubbed “Black October”. Cybersecurity teams are in a high-stakes race against threat actors who are leveraging automated AI agents to scan and instantly exploit critical software vulnerabilities across thousands of targets simultaneously.
The major cyber incidents and disruptions unfolding over the past few hours include:
Global scurry to protect the Web: Critical PHP flaws xxploited
A massive wave of automated attacks is actively striking servers worldwide following the disclosure of major vulnerabilities in ‘PHP’, a core programming language behind a massive portion of the internet.
- The Impact: Cloud infrastructure provider Cloudflare has recorded millions of exploit attempts.
- Defensive Action: Government agencies, police forces, hospitals, and major enterprise corporations across the Netherlands, France, Denmark, and Finland have proactively taken their official websites and digital platforms entirely offline to buy time to deploy emergency patches.
Major waves of infrastructure attacks buffet Japan
A continuous wave of cyberattacks has severely disrupted internet and business services across the Japanese economy.
- The Impact: Multiple high-profile Japanese corporations have experienced extensive service outages.
- The Latest: Over the past few hours, affected companies have officially moved to pay out financial compensation to users whose services were heavily disrupted, raising massive concerns regarding regional economic stability.
Political targeting: Italian Prime Minister’s email hit
Government cyber defenses have been triggered in Italy following a highly targeted intrusion attempt.
The Impact: A breach directly targeted the email systems of the Italian lower house of parliament, specifically compromising accounts belonging to Prime Minister Giorgia Meloni. Investigation into the source and the extent of data accessed is ongoing.
Direct target campaign against Starlink users
Reports have surfaced outlining a highly sophisticated, heavy cyber espionage campaign actively targeting users of Elon Musk’s satellite network.
The Impact: Intel and industry sources have traced the aggressive targeting back to a notorious, alleged Israeli private intelligence and surveillance firm, which is systematically targeting Starlink users to intercept or monitor secure communications.
Automated AI malware unveiled (“CyberStrikeAI”)
In the past few hours, researchers have shed light on the exact mechanics causing this massive spike in breaches. Threat actors are officially utilizing a newly detected framework named ‘CyberStrikeAI’.
The Threat: This framework coordinates 44 interconnected AI agents designed to fully automate the hacking process, identifying network entry points, drafting custom malicious code, and executing data theft natively without requiring human intervention.
.