AI discovered PHP vulnerability forces 32 UK Government websites offline.
3 min read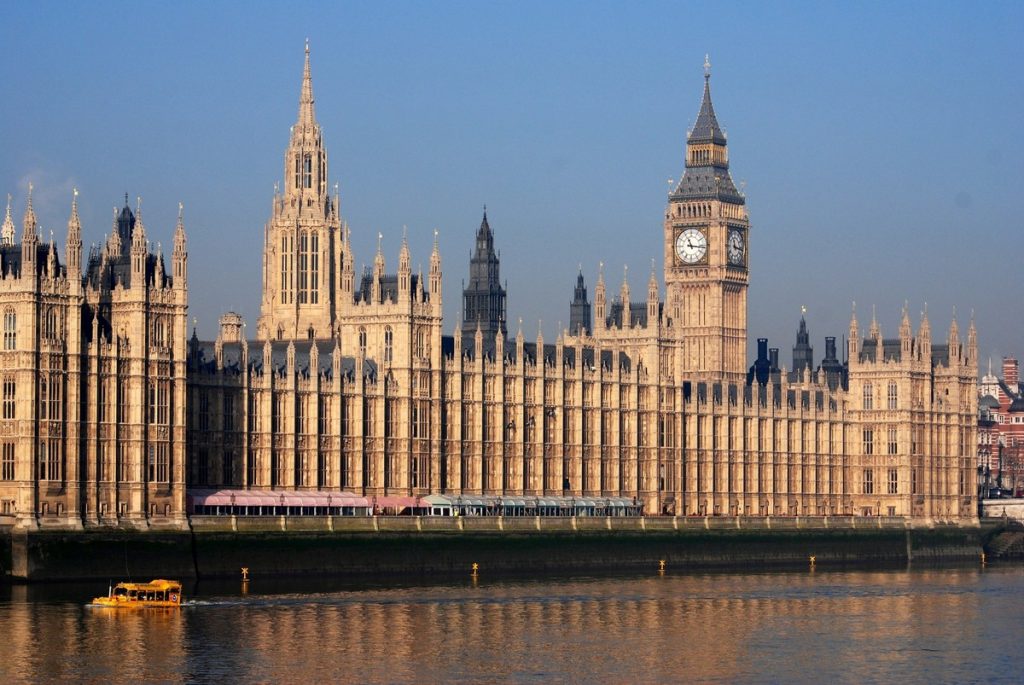
On October 22, 2026 A massive global cybersecurity scramble is underway after two critical vulnerabilities discovered in the PHP programming language forced at least 32 government services and websites offline.
The flaws, which are being described by experts as some of the most severe in software history, were uncovered using cutting-edge Artificial Intelligence models developed by cybersecurity firms Wiz and Calif alongside OpenAI. The discovery has sent IT teams worldwide into a frantic race to apply security patches before hackers can exploit the bug at a global scale.
What is the PHP Vulnerability?
PHP is an open-source programming language that underpins roughly 70% of the world’s identifiable websites, powering everything from small blogs to major enterprise systems and public sector portals.
On Wednesday, October 21, PHP developers released emergency fixes for two long-standing security flaws. Rated a staggering 9.2 out of 10 on the CVSS severity scale, the vulnerabilities allow for unauthenticated remote code execution (RCE).
This means that an attacker could theoretically send commands, steal data, or completely compromise a vulnerable server from afar, all without requiring a password or login credentials. Cybersecurity firm Wiz noted that these flaws rank among the most severe vulnerabilities ever discovered by AI tech.
Why are Government Websites Going Dark?
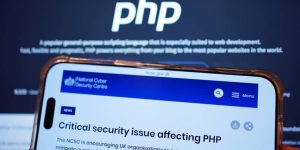
Because PHP is so deeply woven into the fabric of the internet, the European Union’s cybersecurity team (CERT-EU), the UK’s National Cyber Security Centre (NCSC), and other global agencies issued urgent guidance: if you cannot apply the security patches immediately, take your websites offline.
As a direct result of this precautionary advice, a cascading wave of digital shutdowns has occurred:
- 32 Government Services Offline: Ministers have confirmed that dozens of vital public services have been preemptively powered down to isolate them from threat vectors.
- Affected Nations: Public web services have been temporarily shuttered or disrupted across Europe, including the governments of Finland, the Netherlands, France, and Belgium. In a telling sign of the severity, the Dutch National Cybersecurity Agency even took its own website offline to protect its internal architecture.
- Local Authorities & Public Utilities: Beyond national agencies, the outages have hit local governments like the Edinburgh Council, public broadcasters like the BBC, and public infrastructure including a hospital in Antwerp.
Officials emphasize that taking websites offline is a proactive, strategic decision. It is far cheaper and safer to withstand a temporary outage than it is to remediate a fully compromised government database.
Millions of Hacking Attempts Detected
The threat is far from theoretical. While cybersecurity agencies report there is no evidence yet of the flaw being successfully exploited on a significant scale, automated attacks are already surging.
Amazon’s security chief, CJ Moses, revealed that tech giant Amazon’s security team detected attempts to exploit the vulnerabilities against its decoy “honeypot” systems as early as October 17, four days before the public disclosure took place. Hackers have since launched millions of cyber attack attempts across the internet as they scan the web for unpatched servers.
What Does This Mean for Your Website?
If you run an online business or manage a digital platform, you might be wondering if you are at risk.
Do I need to change my passwords?
No. This is a fundamental flaw in the server architecture itself, not a credential leak. Changing your individual user passwords will not protect a server running an outdated version of PHP.
Is my website safe?
Large hosted ecosystems are moving quickly. For instance, Automattic (the operator behind WordPress.com and Tumblr) confirmed that users on its fully managed hosted solutions are safe from the bug.
However, risks remain extraordinarily high for self-hosted websites, small businesses, and organizations running PHP on shared hosting services where customers manage their own environments.
Immediate Action Items for Webmasters:
- Check Your Tech Stack: Determine if your website runs on PHP.
- Apply Patches Immediately: PHP has officially released the version updates that fix these flaws. Work with your hosting provider or developer to deploy them immediately.
- Consider Temporary Downtime: If your site handles highly sensitive user data and you cannot update the patch today, follow the lead of government IT administrators and consider taking the site offline temporarily until it is secured.